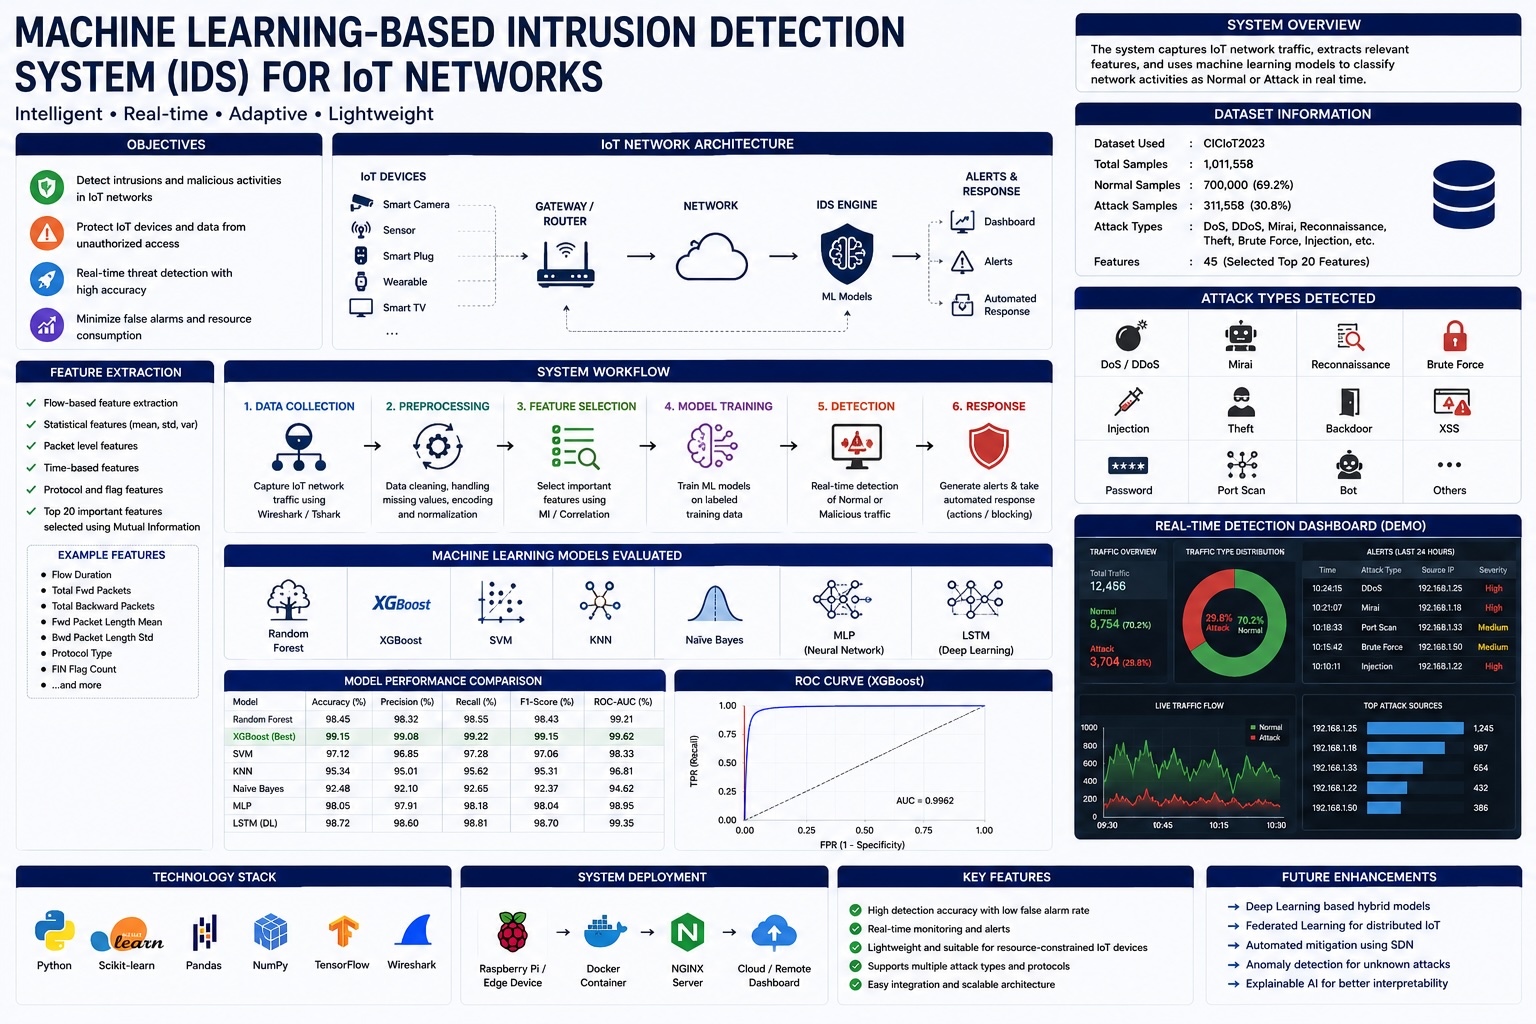
Machine Learning-Based Intrusion Detection System (IDS) for IoT Networks
Description
1. Project Overview
The Internet of Things (IoT) connects billions of smart devices such as:
- Smart home devices
- CCTV cameras
- Smart TVs
- Wearables
- Medical devices
- Industrial sensors
Many IoT devices have limited security features, making them vulnerable to cyberattacks.
This project develops an AI-powered Intrusion Detection System (IDS) that continuously monitors network traffic and automatically identifies malicious activities before they compromise the network.
2. Problem Statement
Traditional signature-based security systems can only detect known attacks.
Modern IoT networks face:
- DDoS attacks
- Botnet attacks
- Malware infections
- Port scanning
- Man-in-the-Middle attacks
- Brute-force attacks
Machine Learning can learn network behavior and detect both known and unknown threats.
3. Project Objectives
Primary Objectives
- Monitor IoT network traffic.
- Detect malicious activities.
- Classify attack types.
- Generate security alerts.
Advanced Objectives
- Real-time attack detection.
- Anomaly detection.
- Threat severity prediction.
- Automated response system.
Attack Types
- DoS
- DDoS
- Man-in-the-Middle
- Botnet Attacks
AI Techniques
- Anomaly Detection
- Deep Learning
- Random Forest
Applications
- Smart homes
- Industrial IoT
Free Datasets
CIC IoT Dataset
https://www.unb.ca/cic/datasets/iotdataset-2023.html
TON-IoT Dataset
https://research.unsw.edu.au/projects/toniot-datasets
Pre-requisites
AI Techniques
- Anomaly Detection
- Deep Learning
- Random Forest
Apply for this Project
Please login to apply for this project and access full features.
Login to Apply